NCA, SAMA & CST Cybersecurity Compliance Services
Build Compliance Around the Frameworks That Apply to Your Business.
Cybersecurity Compliance
Frameworks.
Saudi organizations operate within different cybersecurity regulatory environments depending on their sector, criticality, technology services and regulatory relationships. Nour Solutions helps organizations identify the frameworks that apply to them, assess their current security posture, close compliance gaps and build an evidence-driven cybersecurity program.
Our consulting approach covers NCA cybersecurity controls, SAMA cybersecurity requirements and the CST Cybersecurity Regulatory Framework (CRF), with practical support across governance, risk, policies, controls, evidence and assessment readiness.
A regulatory programme needs both a structure and a check. Cybersecurity GRC consulting builds the governance the controls sit in, and cybersecurity assessment and audit tests readiness before a formal assessment rather than during one.
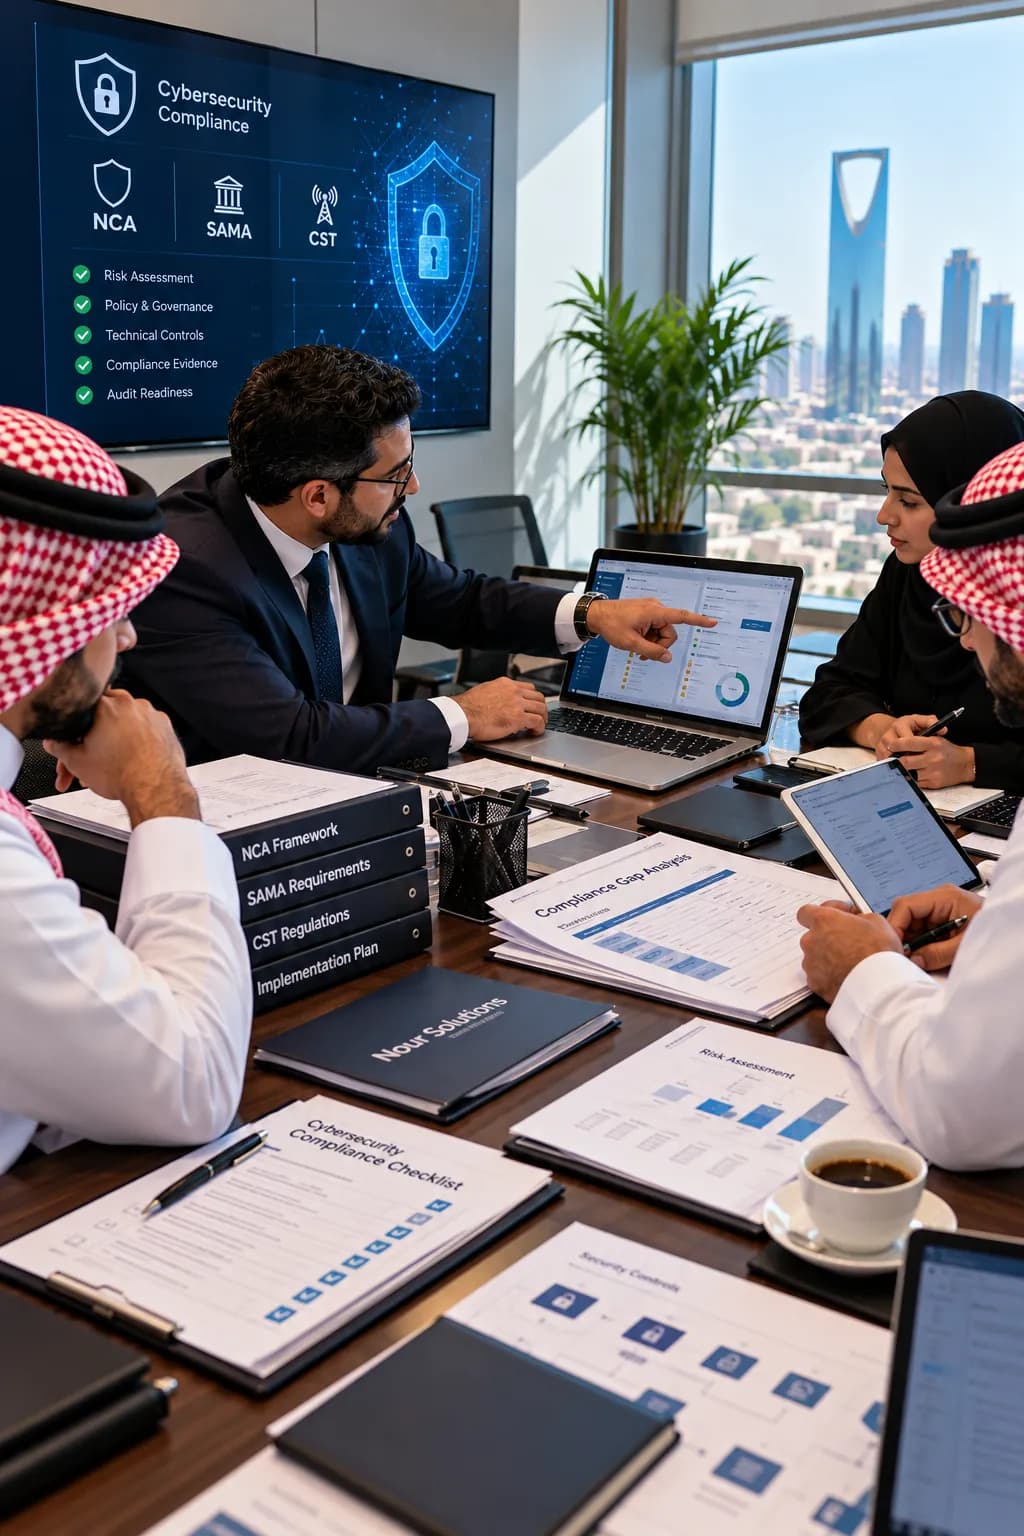
Saudi Regulatory Cybersecurity Expertise in One Engagement
Instead of treating each framework as an isolated compliance project, Nour Solutions can map overlapping requirements into one coordinated compliance program. This helps organizations reduce duplicated documentation, align shared controls and maintain a clearer view of risk, ownership and evidence.
The exact framework scope depends on the organization. NCA requirements can vary by sector and technology environment; SAMA requirements apply to SAMA-regulated financial institutions; and CST-CRF focuses on applicable organizations in the communications and information technology sector.
Frameworks We Support
| Framework | Primary Applicability | Nour Solutions Support |
|---|---|---|
| NCA Cybersecurity Controls | Government, critical national infrastructure and other organizations to which specific NCA controls apply; other organizations may also use them as best practice. | Gap assessment, framework mapping, implementation, evidence, assessment readiness |
| SAMA Cyber Security Framework | Financial institutions regulated by the Saudi Central Bank. | Maturity assessment, control implementation, governance, evidence and regulatory readiness |
| CST Cybersecurity Regulatory Framework (CRF) | Applicable licensed or registered service providers in the ICT sector regulated by CST. | Readiness assessment, control alignment, documentation, implementation and audit support |
NCA Cybersecurity Compliance
The National Cybersecurity Authority (NCA) publishes cybersecurity controls and supporting guidance for organizations in Saudi Arabia. The current Essential Cybersecurity Controls are listed by NCA as ECC 2-2024. NCA also publishes specialized control sets for areas such as critical systems, data, operational technology, cloud and telework.
NCA Framework & Control Support
- NCA Essential Cybersecurity Controls (ECC)
- Critical Systems Cybersecurity Controls (CSCC)
- Data Cybersecurity Controls (DCC)
- Operational Technology Cybersecurity Controls (OTCC)
- Cloud Cybersecurity Controls
- Telework Cybersecurity Controls (TCC)
- Applicable NCA implementation guides and assessment tools
We help organizations determine which NCA controls are relevant, assess current compliance, map existing controls and prioritize remediation. The exact applicability is determined by the organization's sector, systems, technologies and regulatory context.
SAMA Cybersecurity Compliance
The SAMA Cyber Security Framework provides a common approach for cybersecurity governance, risk management and control maturity within SAMA-regulated financial institutions. SAMA states that regulated member organizations must adopt the framework and use it to assess cybersecurity control maturity and effectiveness.
SAMA Compliance Support
- SAMA Cyber Security Framework (CSF)
- Minimum Verification Controls (MVC)
- Cyber Resilience Fundamental Requirements (CRFR)
- Cybersecurity governance and oversight
- Risk management and compliance
- Security operations and technology
- Third-party cybersecurity
- Maturity assessment and improvement planning
Our support is designed for banks, insurers, financing companies and other SAMA-regulated organizations that need a practical route from current maturity to the level required by their regulatory obligations. SAMA's framework is structured around governance, risk and compliance, operations and technology, and third-party cybersecurity.
CST Cybersecurity Compliance
The Communications, Space & Technology Commission (CST) Cybersecurity Regulatory Framework (CRF) establishes cybersecurity requirements for applicable service providers in the ICT sector. CST's framework is intended to raise cybersecurity maturity among organizations regulated or supervised by CST.
CST-CRF Compliance Support
- Service-provider classification and scope review
- CST-CRF gap assessment
- Cybersecurity governance and policy development
- Risk management and control alignment
- Technical security control readiness
- Compliance documentation and evidence
- Assessment preparation and coordination
- Remediation and finding closure
CST's published framework uses a service-provider classification process to determine the level of compliance required. We help organizations prepare the applicable requirements based on their classification and CST obligations.
Our NCA, SAMA & CST Compliance Services
Gap & Maturity Assessment
Assess the current cybersecurity posture against the applicable framework, identify gaps and establish a prioritized improvement roadmap.
Cybersecurity Risk Assessment
Identify assets, threats, vulnerabilities and business impact; score risks and develop treatment plans aligned with regulatory requirements.
Governance, Policies & Procedures
Develop and align cybersecurity policies, procedures, roles, responsibilities, committees and governance mechanisms.
GRC Documentation & Evidence
Build control mappings, risk registers, compliance records, evidence repositories and management reporting that can be maintained by the client.
Control Implementation & Remediation
Support technical and administrative control improvements across identity, endpoint, network, cloud, monitoring, vulnerability management, incident response and third-party security.
Audit & Assessment Preparation
Prepare teams, documentation and evidence for regulatory reviews, external assessments and internal assurance activities.
Finding & Observation Closure
Analyze findings, identify root causes, define corrective actions and prepare evidence for closure.
Ongoing Compliance & Advisory
Provide periodic compliance reviews, policy updates, evidence maintenance, risk tracking, training and technical guidance to help sustain the program.
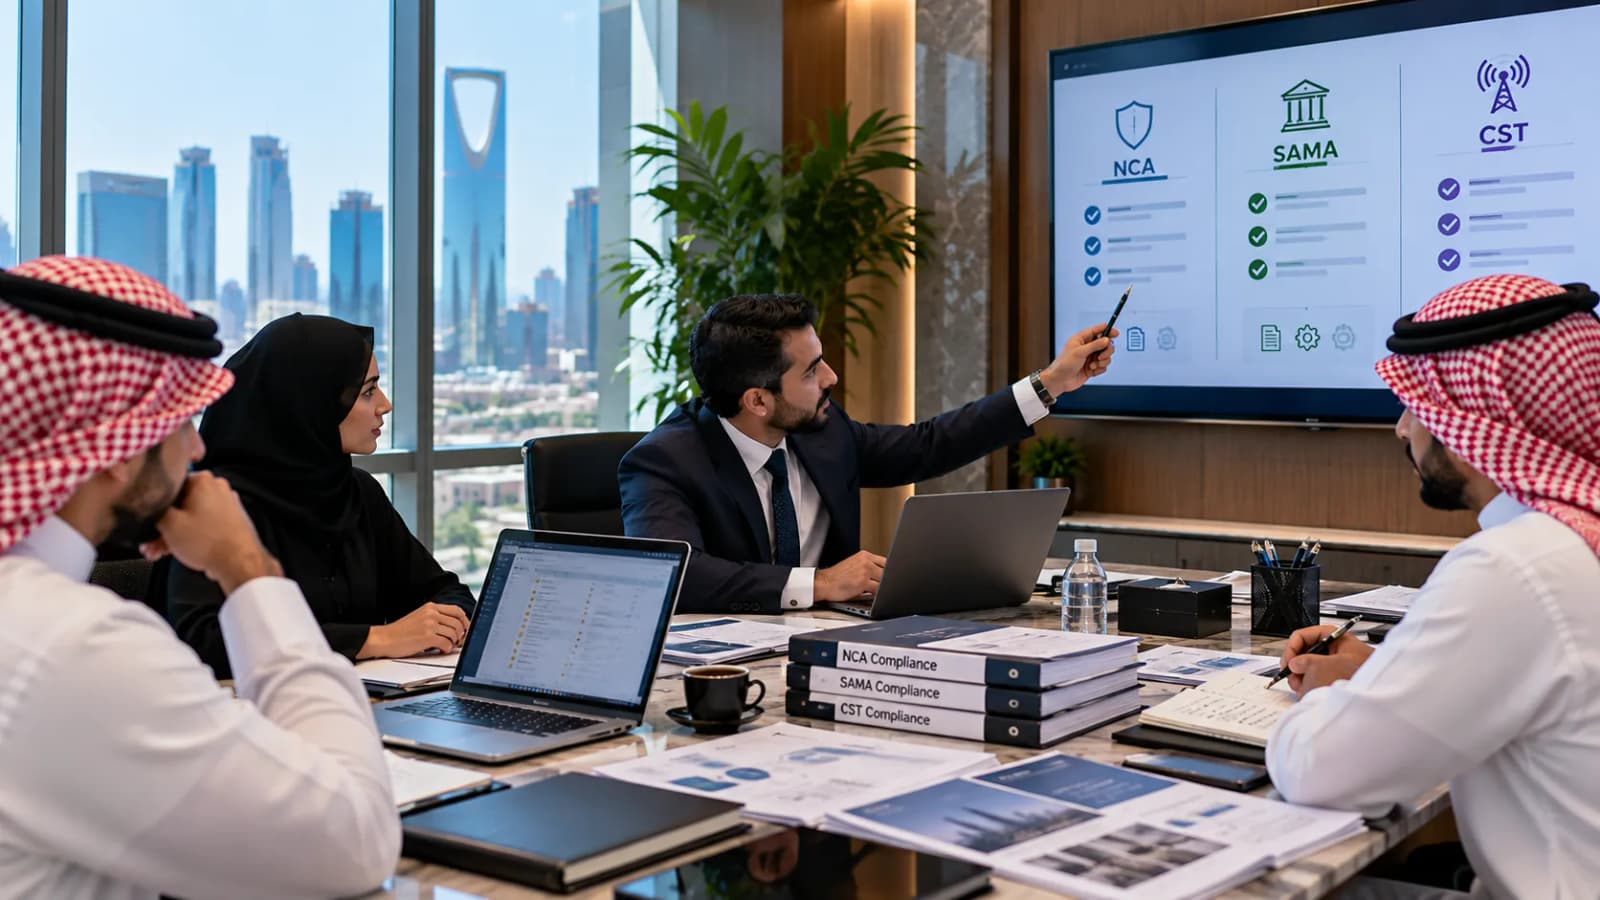
A second view of the same work: a consultant talking a document through with a client team at a table. Landscape, daylight, no staged handshakes.
One Control Framework, Multiple Regulatory Requirements
NCA, SAMA and CST requirements are not interchangeable, but many cybersecurity practices overlap. Nour Solutions can build a common control foundation and then map the organization-specific requirements on top of it. This can reduce duplicated effort while preserving the evidence needed for each regulator.
- One cybersecurity governance structure
- Shared risk-management methodology
- Centralized policy and document management
- Cross-framework control mapping
- Reusable evidence where the framework permits
- Separate regulatory gap tracking and reporting
This unified approach is consistent with how leading Saudi cybersecurity consultancies position cross-framework programs: map overlapping controls once, then maintain the specific evidence and maturity requirements of each applicable framework.
Our Compliance Delivery Approach
- Scope — Identify the organization, sector, regulatory relationship, systems and applicable frameworks.
- Assess — Perform gap, maturity and risk assessments against the relevant requirements.
- Map — Connect existing controls, policies and evidence to the applicable framework.
- Prioritize — Build a practical remediation roadmap based on risk, regulatory priority and business impact.
- Implement — Improve governance, documentation and technical controls.
- Validate — Review evidence, test controls and prepare teams for the assessment or regulatory review.
- Close — Address findings and strengthen the controls that require further improvement.
- Sustain — Continue periodic compliance reviews, evidence maintenance and advisory support.
Who We Support
- Government and government-related organizations
- Critical and regulated organizations
- Banks, insurers and financial institutions regulated by SAMA
- ICT service providers and other CST-regulated organizations
- Technology and cloud service providers
- Organizations subject to NCA cybersecurity controls
- Companies preparing for customer or regulatory cybersecurity assessments
Why Choose Nour Solutions?
- Saudi-focused cybersecurity compliance expertise.
- Cross-framework capability across NCA, SAMA and CST environments.
- Compliance and technical implementation support through one partner.
- Evidence-driven documentation designed around real operating processes.
- Risk-based remediation rather than checklist-only consulting.
- Practical support from initial assessment through ongoing compliance.
Common Compliance Challenges We Help Solve
- Unclear framework applicability or scope
- Policies that are outdated or not implemented
- Controls that exist but lack evidence
- Incomplete risk registers and treatment plans
- Weak third-party risk management
- Insufficient monitoring and incident-response evidence
- Uncoordinated compliance projects across different frameworks
- Findings that remain open because ownership or remediation evidence is unclear
Ready to Strengthen Your Regulatory Cybersecurity Posture?
Whether you are preparing for NCA requirements, a SAMA cybersecurity assessment or CST-CRF compliance, Nour Solutions can help you understand what applies, identify the gaps and build a practical path to stronger cybersecurity governance and assessment readiness.
Questions about this service?
Speak with a consultant about your requirement.
Frequently Asked
Questions.
What is NCA cybersecurity compliance?
NCA cybersecurity compliance means implementing the NCA controls that apply to the organization and being able to demonstrate those controls through appropriate governance, processes, technical safeguards and evidence. NCA publishes a range of control sets, so applicability should be assessed rather than assumed.
What is the NCA ECC?
The Essential Cybersecurity Controls (ECC) are NCA's baseline cybersecurity controls. NCA currently lists ECC 2-2024 and related implementation guidance.
Who needs to comply with SAMA CSF?
The SAMA Cyber Security Framework applies to financial institutions regulated by the Saudi Central Bank, including the member organizations defined by SAMA's framework.
What is CST-CRF?
The CST Cybersecurity Regulatory Framework is a cybersecurity framework for applicable service providers in the information and communications technology sector regulated by CST.
Can one compliance program cover NCA and SAMA requirements?
Many controls can be managed through a shared governance and control structure, but the frameworks remain separate and applicability-specific. We can map overlapping requirements while maintaining the evidence and maturity requirements of each framework.
Do you provide NCA, SAMA and CST gap assessments?
Yes. We assess the current posture against the applicable framework, identify gaps and develop a prioritized remediation roadmap.
Can Nour Solutions help with audit findings?
Yes. We can support root-cause analysis, corrective-action planning, remediation and evidence preparation for applicable follow-up activities.
Do you provide ongoing compliance support?
Yes. Ongoing support can include periodic reviews, risk and evidence maintenance, policy updates, training, management reporting and technical control guidance.