
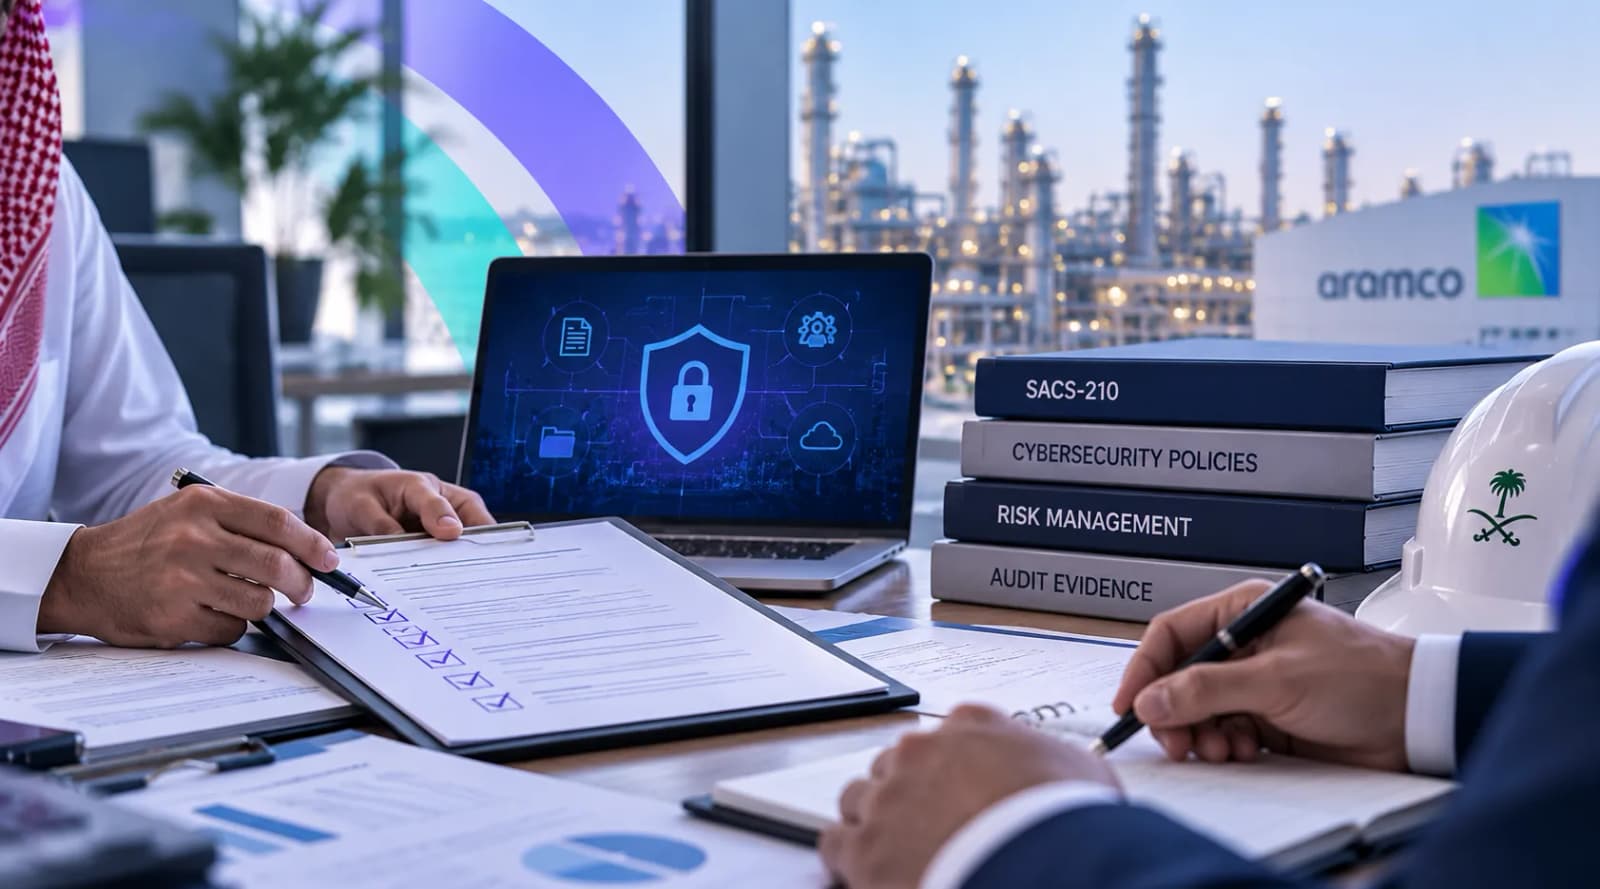
For companies supplying Saudi Aramco, cybersecurity compliance is an important part of supplier qualification and ongoing business requirements.
The Aramco Cybersecurity Compliance Certificate (CCC) verifies that suppliers meet applicable cybersecurity requirements under Saudi Aramco's Third-Party Cybersecurity Standard, SACS-210.
Whether your company is applying for certification for the first time or preparing for renewal, this guide explains the Aramco CCC requirements, documentation, assessment process, and practical steps to prepare.
What Is Aramco CCC Certification?
The Aramco Cybersecurity Compliance Certificate is part of Saudi Aramco's Third-Party Cybersecurity Compliance Program.
It is designed to ensure that suppliers and contractors implement appropriate safeguards to protect information, systems, and services connected to Aramco operations.
The program follows SACS-210, the Third-Party Cybersecurity Standard updated in February 2026.
The standard includes general cybersecurity requirements and additional controls based on the supplier's classification and business activities.
For Saudi Aramco vendors, understanding the applicable classification is the first step toward certification readiness.
Aramco CCC vs. CCC+: Understanding the Difference
Saudi Aramco uses two certification approaches based on the supplier's cybersecurity classification.
| Certificate | Assessment requirement |
|---|---|
| Aramco CCC | Supplier self-assessment with remote verification by an Aramco-authorized audit firm. |
| Aramco CCC+ | On-site cybersecurity assessment conducted by an Aramco-authorized audit firm. |
Under Aramco's published certification guidance, CCC+ applies to suppliers classified under Network Connectivity or Critical Data Processor.
The applicable certification type is determined through the official Third Party Classification process. Suppliers falling under multiple classifications must address the relevant controls for each.
Aramco CCC Requirements Checklist
Before scheduling an Aramco CCC assessment, suppliers should review the following preparation checklist.
1. Confirm Your Supplier Classification
Coordinate with your Aramco department or proponent to obtain the Third Party Classification Template.
Complete the required Classification Confirmation Letter and identify the cybersecurity controls applicable to your company's services.
2. Review the Applicable SACS-210 Controls
Assess your existing cybersecurity practices against the relevant SACS-210 requirements.
The standard addresses areas such as:
- Cybersecurity governance and policies
- Asset management and access controls
- Data protection and encryption
- Network and endpoint security
- Vulnerability and patch management
- Security monitoring and incident response
Additional requirements may apply depending on your classification.
3. Prepare Cybersecurity Policies and Procedures
Ensure your organization has documented and implemented the policies required by the standard.
These may include acceptable use, access management, asset management, incident response, secure data disposal, and business continuity procedures.
Documentation should reflect actual business practices rather than policies created solely for assessment.
4. Verify Technical Security Controls
Review whether the required security measures are implemented and functioning.
Important areas include multi-factor authentication, endpoint protection, secure email configuration, access restrictions, encryption, logging, and patch management.
For example, SACS-210 includes requirements for MFA on remote access, cloud services, and privileged accounts.
5. Organize Supporting Evidence
Aramco CCC certification requires evidence demonstrating that cybersecurity controls are implemented.
Depending on the applicable controls, supporting evidence may include:
- Approved cybersecurity policies
- Asset inventories and access review records
- System configuration screenshots
- Security logs and monitoring records
- Vulnerability and patch management reports
- Incident response and employee training records
6. Conduct an Internal Readiness Assessment
Before the formal assessment, perform a cybersecurity gap review against the applicable SACS-210 controls.
Identify missing documentation, ineffective controls, and incomplete evidence. Assign corrective actions and verify that the gaps have been addressed.
An internal readiness review can help reduce avoidable assessment findings and repeated submissions.
7. Prepare for the Authorized Audit
Select an Aramco-authorized audit firm through the official CCC process.
Prepare the completed classification documents, compliance report, and supporting evidence for verification.
The assessment approach will depend on whether your organization requires CCC or CCC+.
How Does the Aramco CCC Assessment Work?
The certification process generally follows these stages:
- Classification: Confirm the supplier classification and applicable requirements with the Aramco proponent.
- Preparation: Implement the relevant SACS-210 controls and organize supporting evidence.
- Audit firm selection: Select and engage an Aramco-authorized audit firm through the CCC Portal.
- Assessment: Complete the required remote verification or on-site assessment.
- Certificate submission: Submit the issued certificate and compliance report through Aramco's e-Marketplace system.
Only Aramco-authorized audit firms can conduct the formal certification assessment and issue the applicable certificate.
Aramco CCC Validity and Renewal
According to Aramco's certification program, the CCC is valid for two years from its issuance date, provided the supplier's cybersecurity classification remains unchanged.
Suppliers should begin renewal preparation before their certificates expire.
A new contract involving a classification not covered by the existing certificate may require an additional assessment and a new certificate.
Maintaining updated security policies, technical controls, and supporting evidence throughout the certification period helps make renewal preparation more manageable.
Prepare for Aramco CCC Compliance with Nour Solutions
Preparing for Aramco CCC certification requires a clear understanding of SACS-210 controls, organized documentation, and reliable cybersecurity evidence.
Nour Solutions supports Saudi Aramco suppliers and contractors with cybersecurity gap assessments, compliance documentation, technical remediation guidance, and audit readiness.
Explore our Aramco CCC & CCC+ Compliance Services to learn how we can help your organization prepare for the certification process.
Official References
- Saudi Aramco — Third-Party Cybersecurity Compliance Certificate Program — Certification types, classification and the assessment process.
- SACS-210 Third-Party Cybersecurity Standard (February 2026) — The full standard, as a PDF download.
الأسئلة الشائعة
Is Aramco CCC mandatory for suppliers?
Aramco's CCC program requires third-party suppliers to obtain the applicable cybersecurity certification. The assessment scope and certificate type depend on the supplier's classification.
What is SACS-210?
SACS-210 is Saudi Aramco's Third-Party Cybersecurity Standard. It establishes cybersecurity requirements for suppliers and contractors handling applicable information, systems, connectivity, or services.
How long is Aramco CCC certification valid?
The certificate is valid for two years, subject to the supplier's classification remaining unchanged. Renewal must be completed before expiry.
Can a cybersecurity consultancy issue an Aramco CCC certificate?
No. Cybersecurity consultants can support gap assessments, documentation, remediation, and audit preparation. Formal assessment and certificate issuance are handled by Aramco-authorized audit firms.